MCP Security Threat Model for Production Systems
A practical threat model for MCP hosts, clients, servers, tools, credentials, model context, and downstream systems.
Prompt injection defense, permissions, authentication, authorization, sandboxing, guardrails, and safe agent operation.
A practical threat model for MCP hosts, clients, servers, tools, credentials, model context, and downstream systems.
9 published articles
A practical permission model for controlling which MCP tools users and agents can discover, call, and approve.
A defensive guide to prompt injection, tool poisoning, confused-deputy risks, and data exfiltration in MCP systems.
A production-focused guide to authenticating MCP clients and authorizing users, tools, resources, tenants, and downstream actions.
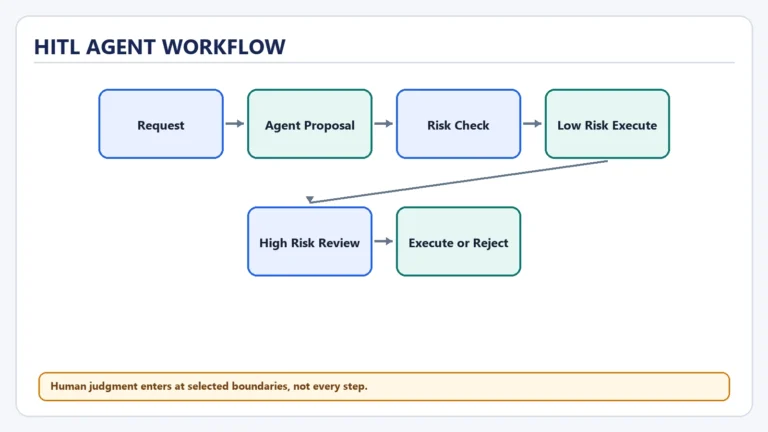
A practical, production-oriented explanation of human-in-the-loop control, with examples, boundaries, trade-offs, and failure handling patterns.
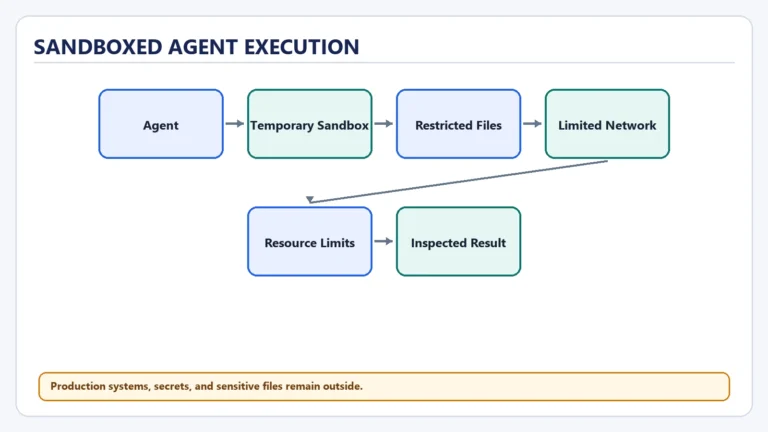
A practical, production-oriented explanation of sandboxed agent execution, with examples, boundaries, trade-offs, and failure handling patterns.
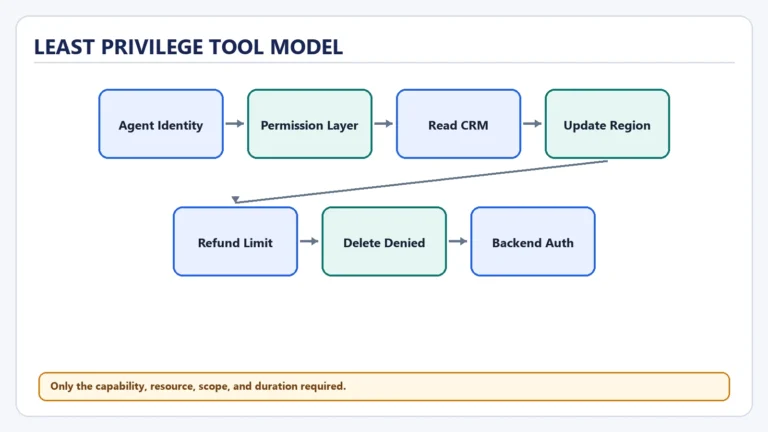
A practical, production-oriented explanation of least-privilege tool permissions, with examples, boundaries, trade-offs, and failure handling patterns.
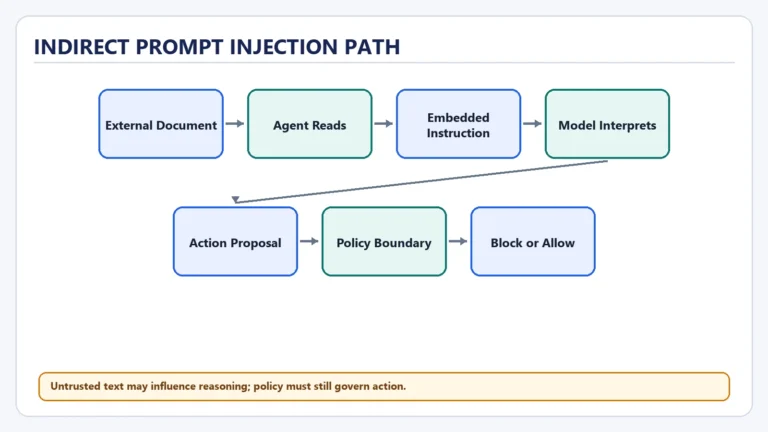
A practical, production-oriented explanation of prompt injection in tool-using agents, with examples, boundaries, trade-offs, and failure handling patterns.
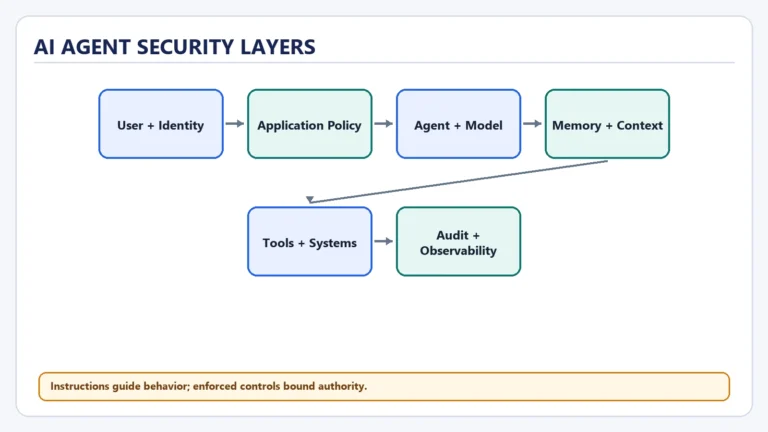
A practical, production-oriented explanation of the security model of an AI agent, with examples, boundaries, trade-offs, and failure handling patterns.