MCP Security Threat Model for Production Systems
A practical threat model for MCP hosts, clients, servers, tools, credentials, model context, and downstream systems.
Everything required to move AI agents from prototypes into secure, observable, reliable, scalable production systems.
A practical threat model for MCP hosts, clients, servers, tools, credentials, model context, and downstream systems.
31 published articles
A practical permission model for controlling which MCP tools users and agents can discover, call, and approve.
A defensive guide to prompt injection, tool poisoning, confused-deputy risks, and data exfiltration in MCP systems.
A production deployment guide for remote MCP servers covering network boundaries, identity, scaling, observability, and rollback.
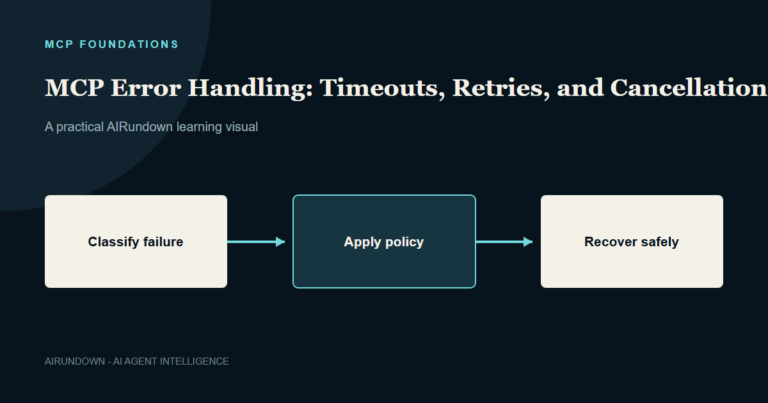
A reliability guide to MCP errors, deadlines, retries, cancellation, progress, idempotency, ambiguous writes, and observable recovery.
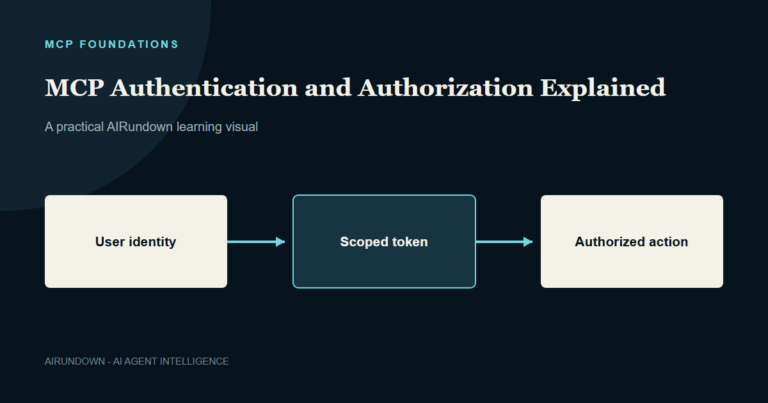
A production-focused guide to authenticating MCP clients and authorizing users, tools, resources, tenants, and downstream actions.
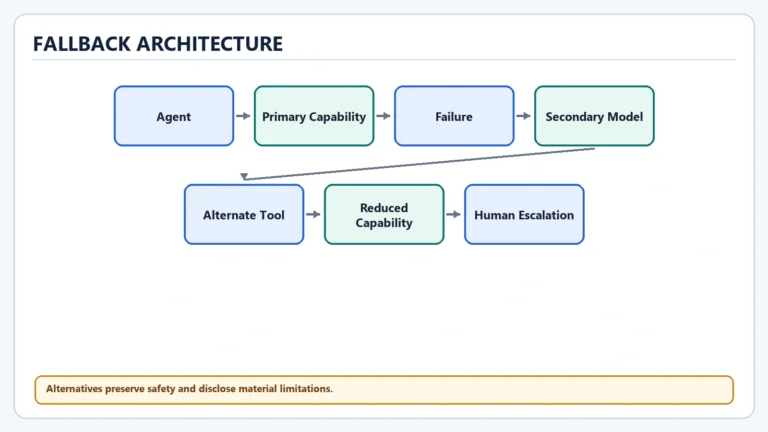
Keep an agent safely useful when models, tools, data, or specialists fail—without fabricating success or silently weakening controls.
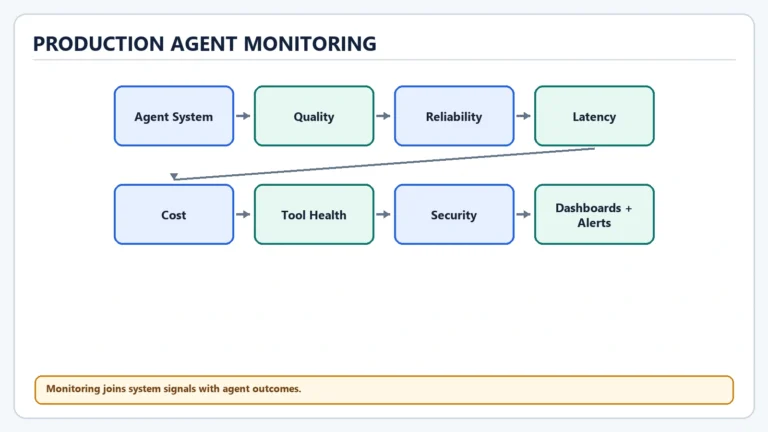
Turn traces, metrics, logs, and evaluations into selected production signals, thresholds, dashboards, and actionable alerts.
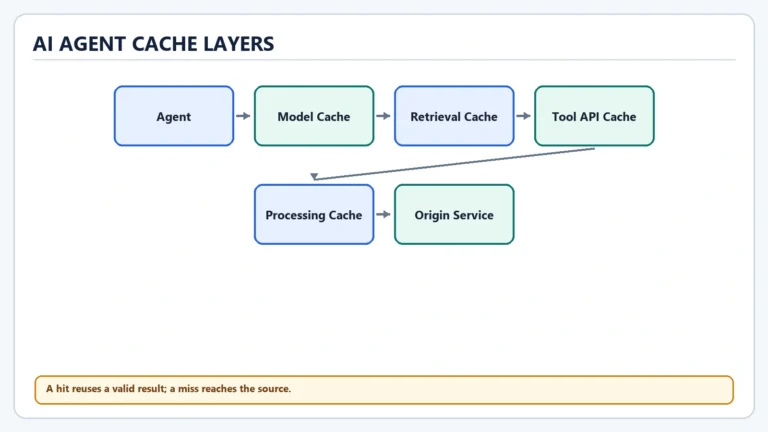
Reuse expensive results only when identity, freshness, authorization, and side-effect semantics make reuse safe.
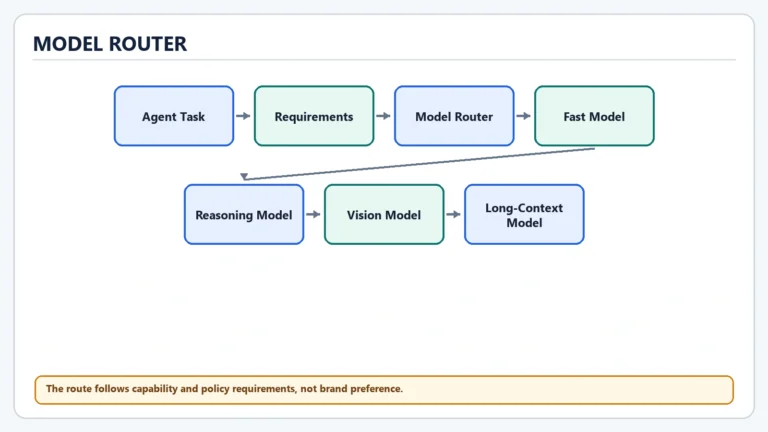
Choose models by task requirements, policy, quality, latency, and cost instead of sending every step to one default.